Identity and Microsoft 365
Conditional Access Without Locking Agents Out
A five-week Entra Conditional Access rollout for a Sherman Oaks brokerage that could not afford a lockout on listing day.
- IndustryReal estate
- WhereSherman Oaks
- Timeline5 weeks
- EngagementConditional Access
Meet the client
A brokerage that had MFA on paper and exceptions in practice
Brokerage name, agent names, listing addresses, and tenant hostnames are withheld at the client's request. The engagement type, method, and constraints are real.
An independent brokerage in Sherman Oaks asked Secure Techies for Conditional Access after an insurer asked how MFA was enforced, not whether it was licensed. We ran policies in report-only, excluded a break-glass account, then enforced MFA and blocked legacy auth without locking agents out of mail on listing day. This was not a FIDO rollout for every phone, and not the nonprofit MFA study.
Primary goals
What the brokerage asked us to produce
Enforce MFA for real
Licenses said MFA was available. Sign-in logs said several agents and a shared mailbox still skipped it.
Do not brick listing day
A lockout at 10 a.m. on a listing is a failed project. They needed report-only evidence before enforce.
Leave a break-glass path
One excluded emergency account, stored offline, not used for daily mail. If Conditional Access misbehaves, the tenant still has a door.
The challenge
They had the license. They did not have the policy.
Microsoft 365 Business Premium was in place. Authenticator was installed for some people. Conditional Access was unused. Legacy protocols still worked. A shared transactions mailbox had no MFA.
- 01
Agents live on personal phones
Most mail happened on BYOD. Full device enrollment would have killed adoption. Conditional Access had to work with the phone they already had.
- 02
Shared mailboxes skipped the control
Transactions and info@ were the accounts that moved money instructions. They were the accounts without MFA.
- 03
Legacy auth was still on
Old IMAP and basic auth paths ignore modern MFA. Leaving them on makes the policy theater.
- 04
Fear of lockout
A prior vendor had flipped a switch on a Friday. The managing broker remembered it. Report-only was how we earned the next click.
How we worked
Five weeks: report-only, then enforce
We treated this as a Conditional Access rollout, not a full Zero Trust program and not a FIDO card for every agent. Scope was written down before any policy went live.
- 01
Read the sign-in logs
Who signed in from where, which apps, which still used basic auth. Out of scope: replacing the MLS, and enrolling every personal iPhone in Intune.
- 02
Build policies in report-only
MFA grant, block legacy auth, named locations for the office. Microsoft's report-only mode shows who would have been blocked without blocking them.
- 03
Fix the exceptions that are real
Shared mailbox, a scanner that still used basic auth, break-glass account. Fake exceptions were removed.
- 04
Enforce in waves
Staff first, then agents, then the shared boxes. Listing-day hours were avoided for the first enforce window.
- 05
Watch the report
Insights and reporting for a week after each wave. Rollback was a named person, not a hope.
What we examined
Six workstreams, one sign-in story
We did not write six unrelated policies. Each workstream fed the same question: can this account skip MFA, and should it.
MFA grant
Require multifactor authentication for user sign-in to Microsoft 365 apps. Microsoft documents the grant in Conditional Access.
Legacy authentication
Block basic auth so MFA cannot be walked around by an old client.
Named locations
Office public IP as a named location for reporting, not as a permanent MFA bypass.
Shared and privileged accounts
Transactions mailbox and admin roles included. Daily mail is not an exception.
Break-glass
One excluded emergency cloud account, long password, stored offline, sign-in monitored.
Report-only and insights
What would have been blocked, then what was blocked, with a person watching the first week.
Report-only showed who would have been blocked. Enforce came after, not before.
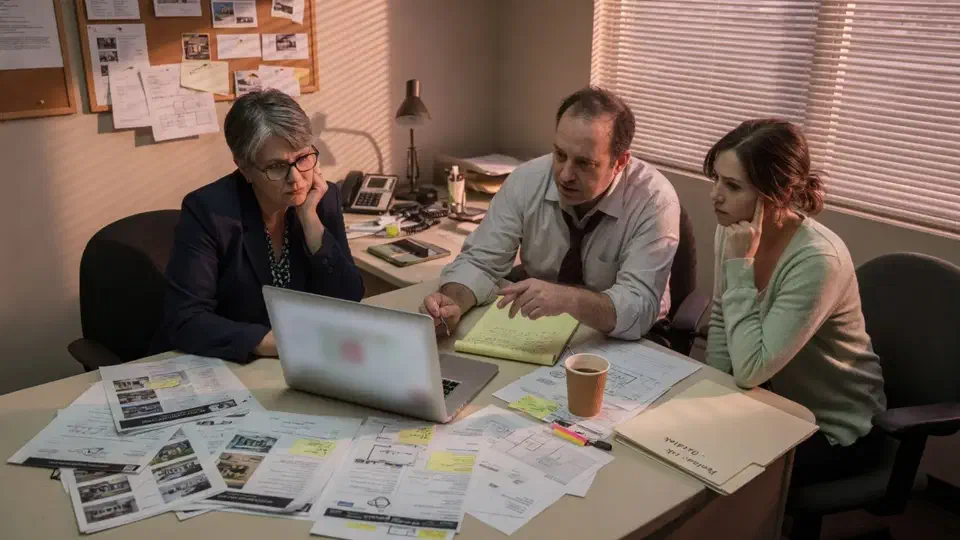
The brokerage had Microsoft 365 licenses that included MFA. Several agents, and the mailbox that handled transaction instructions, still signed in with a password only.
An independent shop in Sherman Oaks asked Secure Techies for Conditional Access after a cyber-insurance form asked how MFA was enforced, not whether Authenticator had been emailed around. They were new to us. A prior vendor had flipped a control on a Friday. The managing broker remembered it.
This case study records how we read the sign-in logs, ran policies in report-only, then enforced MFA and blocked legacy authentication without locking agents out of mail on listing day. Client identifiers stay out. The method does not.
Why the brokerage called
The firm sits in the same pattern as other real estate teams we support: a small office, a large set of personal phones, shared mailboxes that move wiring instructions, and listing days that cannot absorb a lockout. Headcount is not a control. The FTC’s small-business cybersecurity guidance makes that point without a product pitch.
Microsoft’s own primer is the right vocabulary: what Conditional Access is. It is if-then policy for sign-ins. It is not a slogan.
Two facts forced the issue:
- Insurance asked for enforced MFA, including shared mail.
- Sign-in logs showed basic authentication still succeeding for a handful of accounts.
Business email compromise still works when the inbox looks familiar and MFA is optional on the mailbox that handles money language. This brokerage did not have a wire incident on this engagement. They had the mailbox posture that makes those incidents cheap. For the incident-shaped version of that story, see a close call with a fake wire instruction. That client was a law firm. This one is a brokerage. The mailbox problem is related. The policy work is not a copy.
What Conditional Access is, and is not
A Conditional Access policy has assignments and grants. Microsoft documents the policy structure and the grant controls. Require MFA is a grant. Block is a grant. Report-only is how you see the impact before you ruin listing day.
This was not:
- The nonprofit MFA rollout. That study is Authenticator enrollment and a shared finance mailbox. This study is the policy engine around those sign-ins.
- Full Intune of personal phones. Agents would have walked.
- FIDO keys for every agent on day one. Phishing-resistant MFA is a later standard. Microsoft Authenticator was the control they would actually complete.
- A Zero Trust certificate. We do not issue those.
CIS Access Control Management is the public language for joiners, leavers, and MFA. We used it as a completeness check, not as a claim that a 20-person brokerage implemented every CIS safeguard. Brokers already hear “cyber” at conferences. They needed a policy, not another pamphlet.
What this engagement was not
We wrote the non-goals down. If you do not say “report-only first” in the statement of work, someone will ask you to enforce on Friday afternoon.
Out of scope on purpose:
- Replacing the MLS
- Enrolling every personal iPhone
- FIDO for every agent
- Rewriting the wire-callback process as a full BEC program (that can be a later SOW)
In scope:
- Sign-in log review
- Report-only MFA and legacy-auth policies
- Shared mailbox inclusion
- Break-glass
- Waved enforce with help desk coverage
Microsoft explains how to watch impact in Conditional Access insights and reporting. We used that report. We did not invent a “99 percent MFA coverage” graphic.
How we ran the five weeks
Weeks 1 and 2: logs and report-only
We exported who signed in, from which countries, with which clients. Basic auth still worked for a scanner and for one agent on an old mail app. Shared mailboxes were the hole. Microsoft documents why MFA matters at the account: how Entra multifactor authentication works. A policy that skips the mailbox that moves money is not a policy.
Microsoft documents report-only mode as the way to see impact before a policy starts blocking. We used that, not a Friday switch.
We built:
- Require MFA for all users to Microsoft 365 cloud apps, report-only.
- Block legacy authentication, report-only.
- Named location for the office public IP, for reporting, not as a forever bypass.
A week of report-only showed who would have been interrupted. Most were agents who had never finished Authenticator. A few were real exceptions: the scanner, and the break-glass account we had not created yet.
We sat with the office manager and walked the report line by line. Each “would have been blocked” row became either enroll Authenticator, fix the client, or a documented exception. Undocumented exceptions are how the last vendor’s Friday switch happened. If a row could not be explained in one sentence, it was not an exception. It was unfinished enrollment.
We also counted device types. iPhone with Authenticator is a different support call than an old Android mail app. Help desk scripts were written before enforce, not during the first angry listing-day call.
Week 3: exceptions that survive daylight
We created one break-glass cloud admin, long password, stored offline, excluded from Conditional Access, with an alert on any sign-in. Daily mail is not allowed on that account.
The scanner was moved off basic auth or replaced. “The copier needs it” is how tenants stay wide open. If the copier cannot live without basic auth, it does not get a mailbox that also receives wires.
Shared transactions mail got MFA via the people who access it, not via a mythical shared password. Shared mailboxes do not sign in. People do. The policy has to include those people.
Weeks 4 and 5: enforce in waves
Staff in the office first, on a quiet morning. Agents next, not on a listing day. Shared-mailbox accessors last, with help desk on the phone. See managed help desk.
We watched insights after each wave. One agent was blocked because Authenticator had been deleted in a phone swap. That is an expected ticket, not a failed design. We did not roll the policy back for one person. We sat on the phone and finished enrollment.
Sherman Oaks context for ongoing support lives on the Sherman Oaks location page.
What we found
We are not going to invent a “phishing reduced 47 percent” graphic. The useful story is the exceptions.
License is not enforcement. Premium can include MFA. Logs tell you whether it is on.
Shared mail is where money language lives. Skipping it to avoid tickets is how BEC stays cheap.
Legacy auth is a side door. If it is on, MFA is optional for anyone who finds the old path.
Named locations are for reporting first. Using the office IP as a permanent MFA bypass teaches people to only be safe at the desk. Agents are not at the desk.
Break-glass must be boring. If it is used for daily admin, it is not break-glass.
Report-only without a human reading it is theater. The value is the meeting where someone owns each blocked row. A CSV nobody opened is how firms “did report-only” and still locked the office.
One agent will delete Authenticator the week after a phone upgrade. Budget that ticket. Do not budget a rollback of the whole tenant.
How we ranked who to enforce first
A brokerage with twenty agents does not flip every account at 9 a.m. on a Thursday listing.
First wave: office staff who sit near help.
Second wave: agents, after a written notice, not on listing morning.
Third wave: anyone who opens the transactions mailbox.
Later, if they ask: phishing-resistant MFA for admins, app protection on personal Outlook, a tighter named-location story. Not day one.
We pointed them at MFA multi-factor authentication for the user-facing explainer, and at cybersecurity for the email controls that sit next to Conditional Access. Offboarding leftover agent accounts is a related job: employee offboarding IT checklist.
What the brokerage received
- Report-only evidence of who would have been blocked.
- Enforced MFA for Microsoft 365 sign-ins.
- Legacy authentication blocked.
- Shared mailbox accessors included.
- A break-glass account that is not daily mail.
- A week of watched reports after each wave.
What they still did not have, and should not claim:
- FIDO for every agent
- Full MDM of personal phones
- A Zero Trust certificate
- A substitute for call-back on wires
Lessons we would repeat on the next one
Report-only is the project. Enforce is the last week, not the first.
Do not except the money mailbox. That is the whole point.
Staff the help desk on enforce morning. A policy with no one to answer Authenticator questions will be rolled back by the loudest agent.
Break-glass is offline. If it is in the same password manager everyone uses, it is not an emergency door.
Avoid listing day. Construction has punch lists. Brokerages have listing mornings. Know the calendar.
Planning your own Conditional Access rollout
If insurance asked how MFA is enforced and your honest answer is “we sent a link once,” start with sign-in logs and report-only. Bring the tenant admin and whoever owns the transactions mailbox. We will tell you what belongs in the first policy and what belongs in a later FIDO or Intune conversation.
Secure Techies works from Canoga Park with firms across Los Angeles and Southern California. Schedule a consultation if you want the same kind of enforced MFA this client left with, without a lockout story.
For the user explainer, read MFA multi-factor authentication. For a different identity project, see Microsoft 365 MFA without locking out the board. For the insurance questions that usually start this work, see cyber insurance requirements.
Report-only is free in the sense that it does not block. It is not free in staff time. Budget the meeting where someone owns each row. That meeting is the project. If the managing broker will not sit through that report, do not enforce yet. You will spend the next week rolling back. Bring coffee. The meeting is shorter than a lockout. It is not shorter than a skipped report-only week. Put it on the calendar like a listing. Do not hide it in a Friday email.
The outcome
Enforced MFA, without a listing-day outage
- Conditional Access policies enforced for Microsoft 365 after a report-only period
- Legacy authentication blocked
- Shared transactions mailbox included, not excepted
- A documented break-glass account that is not used for daily mail
- No listing-day lockout during the first enforce window
- Clear statement of what this was not: not FIDO for every agent, not full Intune of personal phones, not the nonprofit MFA study
Technologies and frameworks
Related services
Work that sits next to this project
More projects
Other case studies
 Wiping Jobsite Devices the Day a Crew Left
 Microsoft 365 Backup When Retention Was Not Enough
Questions
Frequently asked questions
What is Conditional Access?
Will this lock agents out of mail on listing day?
Is this the same as the nonprofit MFA case study?
Do agents have to enroll their personal iPhones in Intune?
What did the brokerage actually receive?
Need Conditional Access that does not brick listing day?
Secure Techies rolls out Entra Conditional Access for Southern California firms that have the license and still have exceptions. Start with a conversation in Canoga Park.